See the exploit before
it hits your product
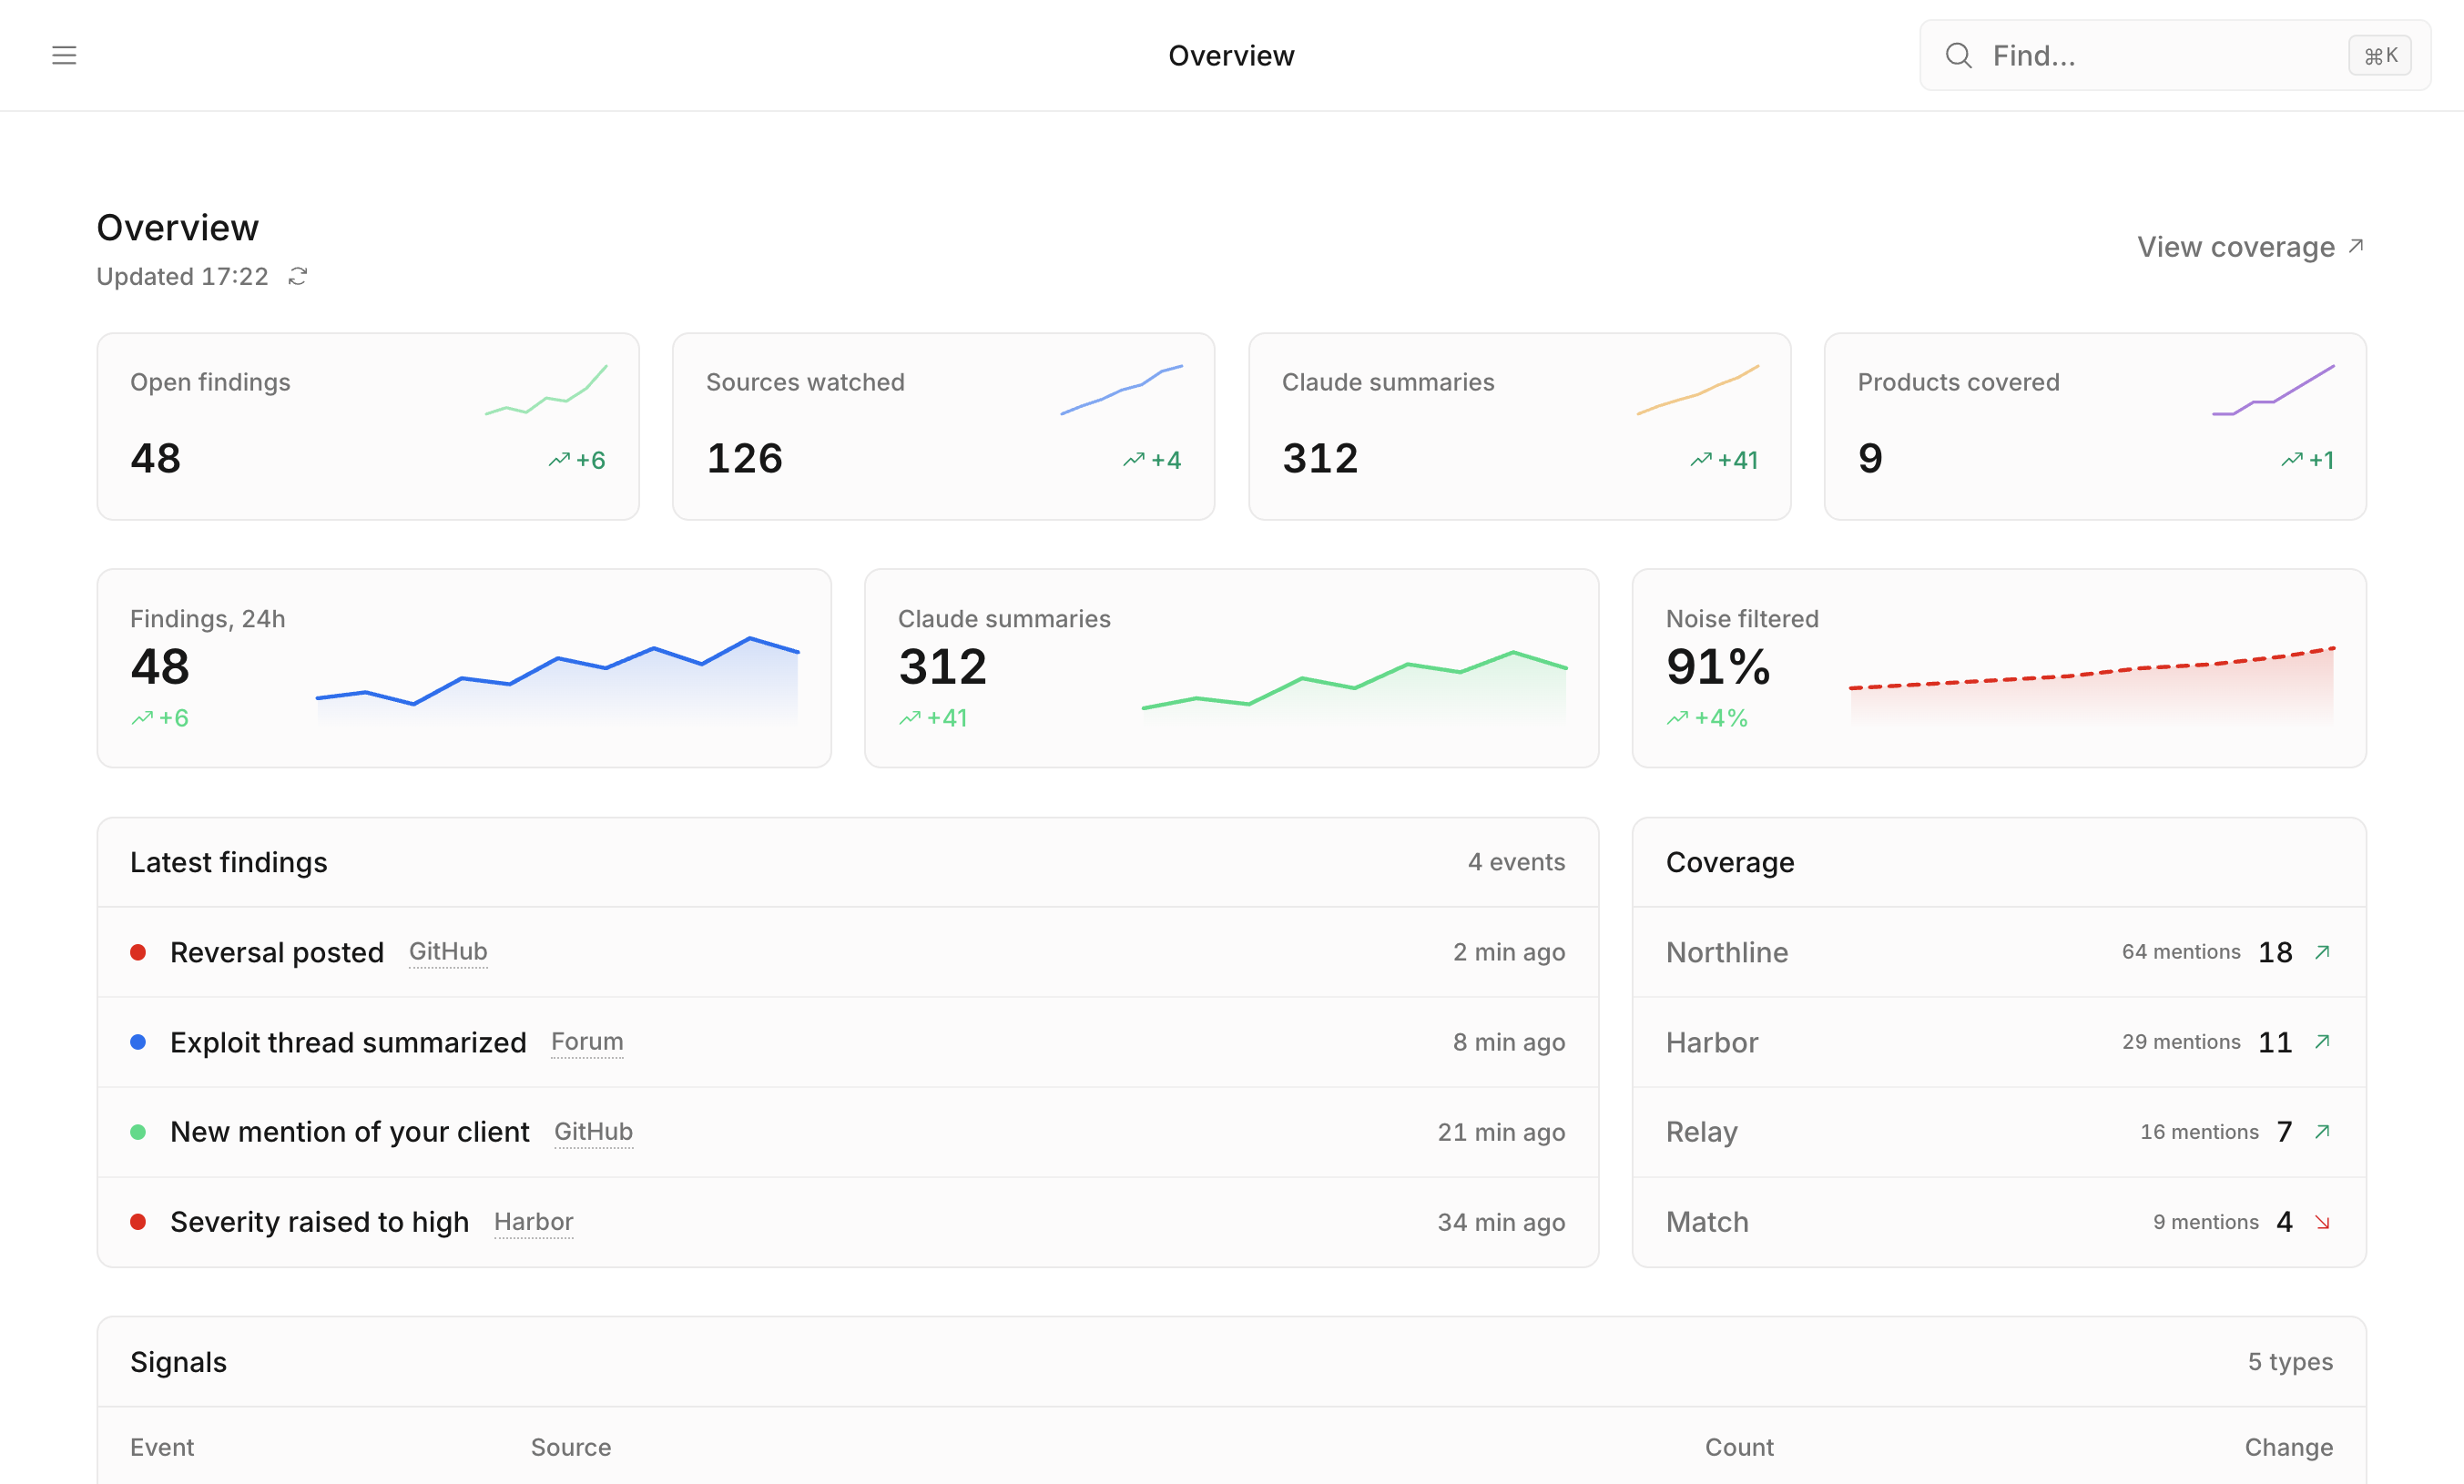
Claude models watch GitHub through game hacking forums, then summarize the threats aimed at your product.
What we watch
Threat intelligence for teams that need to know when their game or the protection around it shows up in the open.
Wide coverage
We monitor sources from GitHub to game hacking forums, plus the malware boards where reversals show up.
Exploit watch
New public exploits against your title are surfaced as they are posted, before they spread through private circles and live sessions.
Reversal detection
When someone publishes a reversal, dump, or breakdown of your product, your security team sees it instead of finding it later.
Claude on the read
Cutting-edge Claude models analyze each find, summarize it, and detect which threats are actually about your product.
Built for studios
Sold to security and live-ops teams, not players. Briefings, coverage scope, and escalation paths are set up for an enterprise program.
Your product, watched
Coverage is scoped to the titles and components you care about, so a new crack or bypass is tied back to the product it targets.
Know when your product is reversed
Tell us the titles you need covered. Claude models summarize what shows up, from GitHub to game hacking forums.